Cybersecurity, AI & Cloud Advisor
Romania
Session Abstract
The grace period is over, and it's not just one law anymore, it's many of them stacked on top of each other. Things like NIS2, DORA, the AI Act, or the CRA, each with its own deadlines, its own auditors, and its own fines, and they're all hitting your desk at the same time. Most companies run a separate program per law: separate owner, evidence, audit, the same control tested four times, and it still misses where the regimes disagree. We'll map where one piece of evidence satisfies NIS2, DORA, the CRA and the AI Act at once, and which controls carry most of the weight. You'll walk away with a practical map of the overlaps, a shortlist of controls that are designed to help you, and a governance plan that builds resilience, not just something to show auditors.
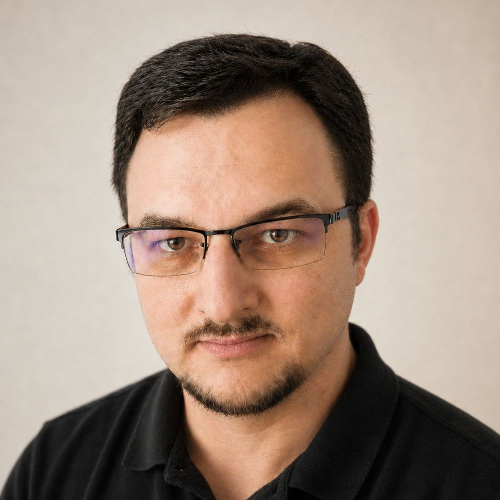
Tudor Damian
With over 20 years in the IT industry, Tudor is a Certified Ethical Hacker and Microsoft MVP who loves everything about technology. As a co-founder of D3 Cyber, he advises organizations on security strategy, AI & Cloud Governance, and EU regulatory compliance (NIS2, DORA, AI Act, CRA). Being a regular presence at local and international events, Tudor combines deep industry experience with a genuine passion for sharing knowledge. After hundreds of talks and training sessions, his goal remains the same: to help IT professionals cut through the noise and build effective strategies dealing with AI-driven threats, Post-Quantum Cryptography challenges, Zero Trust adoption, and an ever-growing EU regulatory landscape.
Tudor can deliver sessions in
Relevant industries
Connect with Tudor

